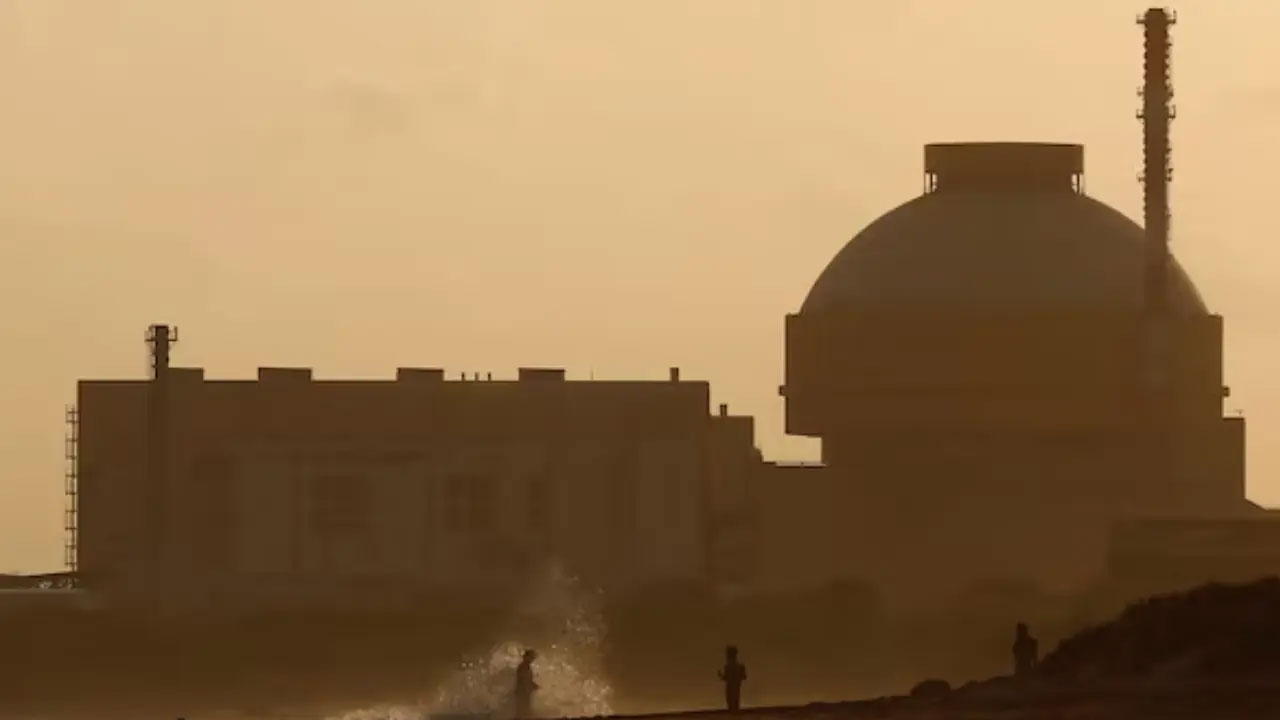
The notorious ransomware group World Leaks has published a large volume of sensitive documents relating to Kudankulam, India’s largest nuclear power plant, on the dark web. The leaked documents include alleged designs of some of the plant’s installations, supplier information, inspection reports, meeting records, equipment evaluations and insurance papers.
Pakistan’s English-language daily Dawn reported on Wednesday (15 July) that Kudankulam, in Tamil Nadu, is the largest of India’s seven nuclear power plants and one of the flagship projects in Prime Minister Narendra Modi’s plan to expand nuclear power generation.
Reliance Group, one of the plant’s contractors, told Reuters that part of its data, stored on a server run by the third-party data-centre service provider Yotta, had been breached. The matter had been reported to the Indian government, the company said, though it did not disclose exactly what data had been leaked.
Reuters reviewed documents dated between 2016 and mid-2025 but could not independently verify their authenticity. Of a total of 8,58,000 Reliance-related files on the World Leaks website, about 19,000 appear to be the most sensitive.
The leaked documents include alleged designs of the ventilation and cooling systems of the under-construction units 3 and 4, the full layout of a common control room, a list of approved suppliers, records of a joint inspection in 2024 and photographs of equipment. One document also claims that insurance has been taken out that would pay $112 million in compensation if units 3 or 4 were damaged in a terrorist attack.
In 2018, Reliance Infrastructure won the contract to build the infrastructure of units 3 and 4. Both units are still under construction and, when commissioned in 2027, are targeted to generate a total of 2,000 megawatts of electricity.
The Nuclear Power Corporation of India and the country’s main cyber-security agency, CERT-In, are investigating the incident. Yotta said it had detected suspicious activity on 29 May, shut it down immediately and thwarted an attempt to run ransomware; but in late June, Reliance said an outside group was claiming a data leak.
Experts say these documents could be used to identify the plant’s support infrastructure, supply chain and security weaknesses, though the published documents contain no information on the core systems of the nuclear reactors supplied by Russia’s state-owned Rosatom.
World Leaks has previously targeted Nike and the Tata Group. Last year, the data of 28.9 million Indian accounts was leaked — the third-highest in the world after the United States and France. In 2019, malware linked to North Korea was also detected in the administrative network of the Kudankulam plant, though authorities said at the time that the plant’s core systems had remained intact.
বাংলায় মূল প্রতিবেদন পড়ুন · Read the original Bengali report